The Compeas Newsroom
Guides, regulatory updates, and company news from Compeas.
Latest
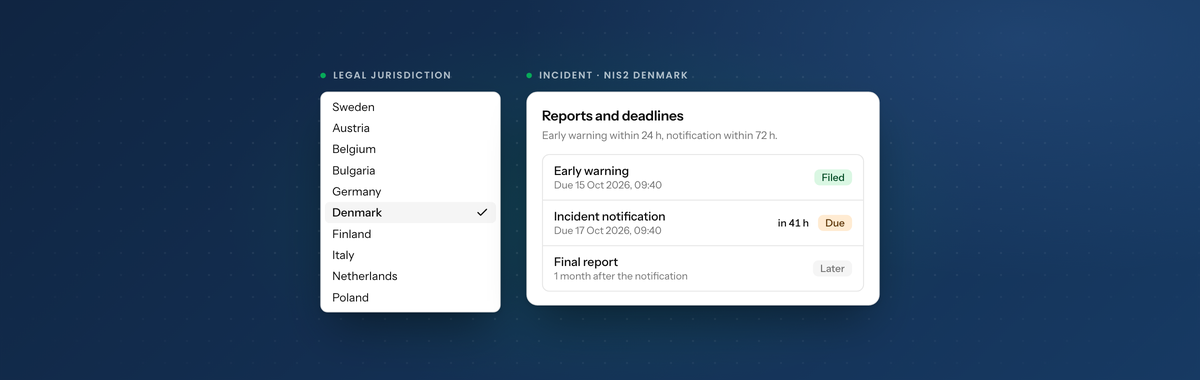
Compeas brings country-specific NIS2 to ten European countries
The October 2026 release adds national NIS2 versions for ten countries, an incident register built around NIS2 reporting deadlines, NIST CSF 2.0 profiles and group-wide oversight in the Auditor Tool.
Read the announcement →How to register: Sweden’s Cybersecurity Act, step by step
Since 1 July 2026 registration goes to the NCSC at FRA, using a form sent by email, and there is no date on which it closes. Assessment, information, form, acknowledgement and updates, in the order they come.
Read the guide →The Cyber Resilience Act’s reporting duty starts 11 September
Manufacturers must report actively exploited vulnerabilities and severe incidents from 11 September 2026 — including for products already on the market. How the duty differs from the Cybersecurity Act in trigger, recipient and clock.
Read the update →Why Traditional GRC Fails
Seven reasons spreadsheets and manual processes break down as organisations grow — from fragmented information to duplicated controls — and what modern governance looks like instead.
Read the guide →NIS2 vs ISO 27001: Which First?
How to choose your first framework based on your market, customers, and timeline — and how control overlap lets you pursue both efficiently.
Read the guide →Automating Evidence Collection
Why manual screenshots and spreadsheets fail audits, and how continuous evidence collection changes the economics of compliance.
Read the guide →Want to hear it first?
One email when we publish something new — or when the next regulatory deadline is approaching. Nothing else.
Rather talk to a person? Get in touch or explore the frameworks.